








Train for the attacks aimed at your business.
Your employees pass the quarterly template and still click real attacks. You get suggested simulations built from this week's public findings about your company.

Learn how global companies are transforming their email security to tackle modern threats

Learn how MSPs can revolutionize their email security and profitably grow their businesses

Secure email gateways and API-based solutions compared for enterprises and MSPs.

Get an overview of our API, Adaptive AI, and Human Element components

Explore the benefits of a mailbox-level, API-driven email security platform

Learn how our Adaptive AI blocks attacks missed by other solutions

See how continuous human insights maximize defense capabilities

Our agents work in concert to anticipate attacks, investigate threats, and educate users

Researches your org like an attacker would, then blocks those threats before they arrive

L2-level forensic investigation across five tracks. Clear verdict in minutes.

Hyper-personalized simulations targeting your highest-risk employees with real OSINT

Stop attacks like BEC, VEC, and VIP impersonation

Continuously protect against malicious links and attachments

Prevent, detect, and respond to ATO attacks in real time

Encrypt outbound email and meet compliance, automatically

Simulations built from what attackers can learn about your business this week, so a hospital's tests look nothing like a bank's.
Template tests measure whether people recognize the test. Your Phishing Simulation Agent starts from what an attacker could find about your organization this week, and an admin approves every launch.
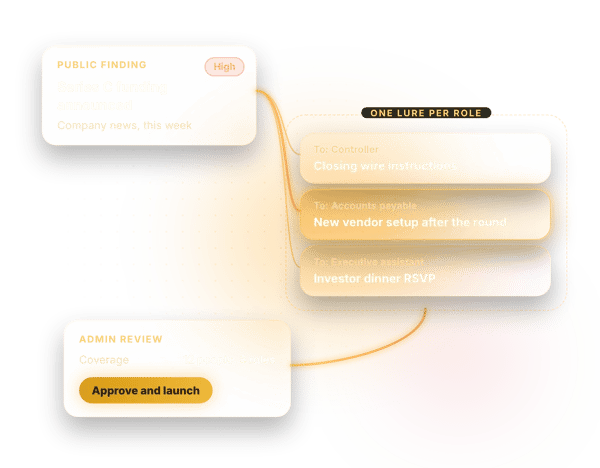
Every week, the agent reads public sources about your organization and scores each finding high, medium or low.
Each finding becomes a suggested simulation. The employees it puts at risk are grouped together, and the lure carries a date after which it goes stale.
Every recipient gets a unique email that fits the finding and their role, so two people in the same campaign never get the same message.
Your admin reviews the suggestions, sees how each one changes awareness coverage, and approves. No one gets more than one simulation a week, existing Ironscales campaigns included.
A click leads straight to a reveal, a training page and a quiz, with up to two reminders until the training is finished.
The dashboard tracks awareness coverage and behavioral risk, with a weekly summary and CSV export for leadership and auditors.
Your employees pass the quarterly template and still click real attacks. You get suggested simulations built from this week's public findings about your company.
A funding round becomes a wire update for finance and a vendor setup for accounts payable. Each lure is themed on your company and varied by role.
Some teams keep clicking. The dashboard shows where awareness lags across the organization, with training and reminders after every click.
Someone asks how awareness is going. You get coverage over the last 90 days, results per simulation, a weekly summary and CSV export.
Training works when it treats people fairly, so the guardrails are built in.
The Red Teaming Agent prepares your defenses for attacks built for you. The Phishing Simulation Agent gets your people ready for the same attacks.
| Template-based awareness | Phishing Simulation Agent | |
|---|---|---|
| Starting point | A library of pre-built templates | What attackers can learn about your organization this week |
| Who gets tested | Everyone, with the same email | The people a finding puts at risk, each with their own email |
| Admin work | Pick templates and build campaigns | Review suggested simulations, approve and launch |
| After a click | Varies | An instant reveal, a training page and a quiz |
| Connected to detection | No | Shares reconnaissance with the Red Teaming Agent |
Already run Ironscales simulations? The agent works alongside them, and your current campaigns count toward the same weekly limit. Agent results also feed the behavioral risk metrics on your Human Risk Management dashboard.
The Phishing Simulation Agent turns what attackers can learn about your organization into simulations written for each employee. It reads public sources every week, suggests simulations, writes a unique email for each recipient and trains anyone who clicks on the spot. An admin approves every launch.
No. The agent suggests simulations and writes the emails, and an admin reviews and approves every launch.
Templates come from a library every customer shares, and everyone gets the same email. The agent starts from what an attacker could learn about your organization this week and writes a different email for each person it puts at risk.
No. No one gets more than one simulation a week, and campaigns you already run in Ironscales count toward the same limit. You can also mark anyone as “never simulate.”
They land on a reveal, a training page and a quiz, with up to two reminders until they finish. The dashboard records who clicked and who reported the email.
It writes in the recipient's language when the impersonated sender would write in it.
Awareness coverage over the last 90 days, behavioral risk such as clicks and serial clickers, results per simulation, and a weekly summary with CSV export.
Your Phishing Simulation Agent gets your people ready for the email an attacker would write for them.