







One Header Named the Attacker's Own Login
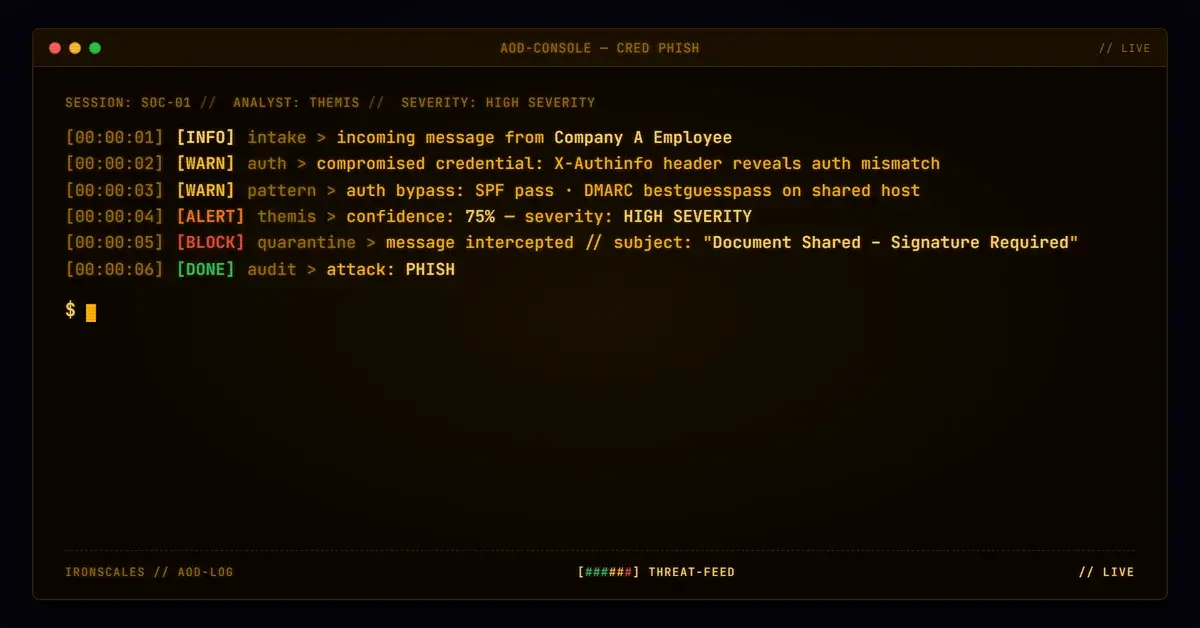
A document-share lure reached four senior mailboxes at a multinational consumer goods group. The sending platform added an X-Authinfo header that logged which account authenticated the SMTP session, and...
Read more